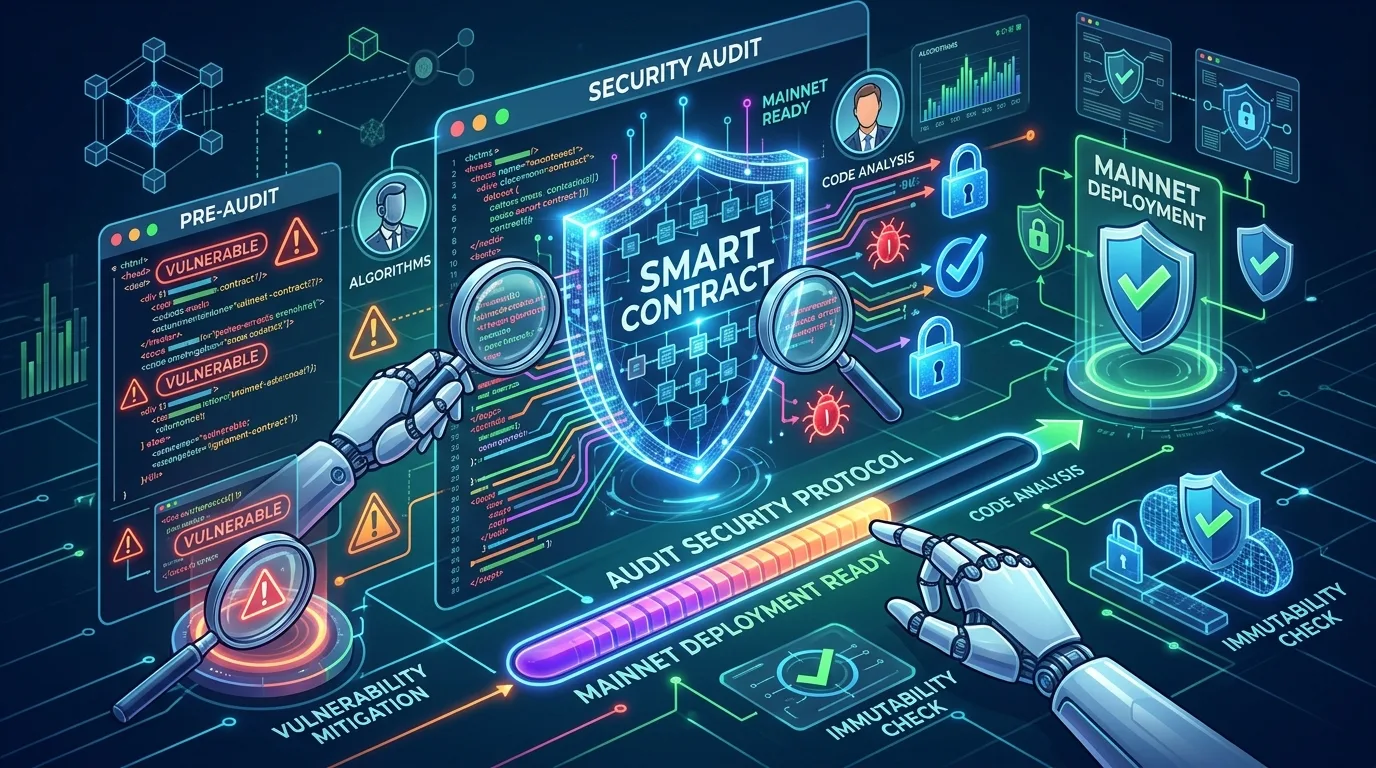
Smart Contract Audits: Why Security Protocols Matter Before Mainnet Deployment
Deploying a smart contract on a live blockchain mainnet is the ultimate milestone for any Web3 project. It marks the transition from conceptual architecture and local testnets to real-world execution handling real financial capital. However, unlike traditional web development—where hotfixes, patch updates, and database rollbacks are standard practice—blockchain environments operate under strict immutability.
Once code is finalized and broadcast to a mainnet, it runs exactly as written. If that code contains a single logic flaw, reentrancy bug, or access control oversight, malicious actors can exploit it within seconds, often siphoning millions of dollars in unrecoverable funds.
A rigorous smart contract audit is not a mere compliance checkbox; it is an indispensable line of defense. Establishing robust security protocols before mainnet deployment is essential for protecting decentralized applications (dApps), preserving capital, and building lasting user trust.
The Core Reality of On-Chain Vulnerabilities
Traditional software development follows a “ship fast, break things, and patch immediately” methodology. Web3 completely flips this paradigm:
-
Immutability Is a Double-Edged Sword: Mainnet smart contracts cannot be edited after deployment. While proxy patterns allow logic updates, improper implementation of upgradeability can introduce serious vulnerabilities, such as storage layout collisions during
delegatecalloperations. -
Public Code and Open State: Smart contract code is open-source and publicly verifiable on block explorers. Hackers use automated scanners, fuzzing tools, and reverse engineering to analyze contracts for exploitable vectors.
-
Instant Economic Consequences: Bugs in Web3 do not just break a user interface or crash a web server—they carry direct financial consequences. Decentralized finance (DeFi) protocols, non-fungible token (NFT) platforms, and bridges frequently hold millions of dollars in automated liquidity pools.
Anatomy of Common Smart Contract Attack Vectors
Understanding why security protocols matter requires examining the exact vectors attackers target when auditing live code:
1. Reentrancy Exploits
A classic attack vector where an external contract calls back into the target contract before the initial state execution finishes. If state variables (like balances) update after transferring funds rather than before, an attacker can drain the contract via recursive withdrawals.
2. Access Control and Privilege Escalation
Functions marked public or external without explicit authorization checks (such as OpenZeppelin’s onlyOwner modifier or role-based access control systems) allow unauthorized actors to execute administrative routines.
3. Oracle Manipulation & Flash Loan Attacks
Protocols that rely on spot prices from single decentralized exchange (DEX) liquidity pools can be exploited via flash loans. Attackers artificially distort pool prices within a single transaction, borrowing assets at inflated valuations or buying them at severe discounts.
4. Integer Overflow and Underflow
While modern Solidity compilers (version 0.8.0 and above) include native arithmetic overflow checks, legacy contracts or low-level assembly blocks (yul) remain susceptible to arithmetic bugs if improperly guarded.
The Complete Multi-Phase Security Protocol Pipeline
A comprehensive security protocol relies on a layered strategy across the entire software development lifecycle (SDLC), rather than treating auditing as an isolated event right before launch.
Phase 1: Pre-Audit Developer Testing
Before handing source code to an independent auditing team, internal developers must complete foundational testing routines:
-
Unit & Integration Testing: Target 100% test coverage using modern testing frameworks like Foundry or Hardhat.
-
Fuzz Testing & Property Testing: Supply randomized inputs to smart contract functions to trigger unexpected edge cases.
-
Static Analysis Tools: Run automated security analyzers (such as Slither or Mythril) to catch low-hanging syntax and structural issues.
Phase 2: Independent Smart Contract Auditing
An external audit involves manual line-by-line review alongside dynamic analysis by dedicated security researchers:
-
Architecture & Specification Review: Ensuring business logic matches the intended system parameters.
-
Manual Code Analysis: Human auditors analyze business logic, governance mechanics, math proofs, and integration dependencies.
-
Formal Verification: Using mathematical tools (such as the Certora Prover) to prove that code adheres to specified invariants under all conditions.
-
Audit Report Delivery: The auditing firm issues a preliminary report categorizing findings by severity (Critical, High, Medium, Low, Informational).
Phase 3: Mitigation & Re-Auditing
The development team remediates identified vulnerabilities, applies fixes, and resubmits the codebase to the auditing firm for final verification and report publication.
Key Differences: Automated Scanners vs. Manual Audits
| Security Dimension | Automated Static Analysis Tools | Independent Manual Audits |
| Speed | Instant (seconds to minutes) | Comprehensive (1 to 4+ weeks) |
| Cost | Free / Low Cost | High investment ($10k – $100k+) |
| Detection Target | Known syntax patterns & standard bugs | Complex logic flaws, economic exploits, & architecture design |
| False Positives | High | Low (curated by human security researchers) |
| Context Awareness | None (analyzes raw code syntax) | High (understands protocol design & business intent) |
While automated tools provide rapid initial checks during development, they cannot evaluate business logic context or complex multi-contract interactions. A combination of automated tooling and manual expert review yields the highest level of contract safety.
Post-Audit Deployment Safeguards
Passing an audit does not guarantee immunity from novel attack vectors. Responsible Web3 teams implement ongoing runtime security controls alongside their pre-deployment protocols:
-
Timelocks and Governance Delay: Enforce multi-day delays on administrative transactions or parameter adjustments to allow users time to exit if malicious changes are proposed.
-
Multi-Signature (Multisig) Controls: Protect administrative keys using multisig setups (e.g., Safe multi-signatures requiring 3-of-5 signers) rather than single Externally Owned Accounts (EOAs).
-
Circuit Breakers (Pause Operations): Build emergency pause functionality into non-critical modules to halt token transfers or deposits if anomalous activity is flagged on-chain.
-
Bug Bounty Programs: Partner with platforms like Immunefi to incentivize ethical hackers to privately disclose newly discovered vulnerabilities.
Deploying to mainnet without passing a formal smart contract audit risks total capital loss, legal liabilities, and permanent project failure. Prioritizing comprehensive auditing protocols before launching code to production is the foundational requirement for building sustainable, resilient Web3 infrastructure.
Discussion (0)
Join the conversation